 ModCodePlus Team
A company website is often the first place where a business processes personal data, and the first place where regulators, competitors and law firms look for mistakes. The good news: most GDPR problems on business websites come from the same few sources and are easy to fix once you know where to look.
This checklist covers the seven points we review on every website we build or take over. It is written for small and medium-sized businesses that serve customers in the EU, whether they are based in Poland, Germany or outside the EU.
This article is a practical overview, not legal advice. For your specific situation, consult a data protection specialist.
1. A privacy policy that matches reality
Many privacy policies are copied from templates. They describe tools the site does not use and miss the ones it does. Under Articles 13 and 14 GDPR, your policy must state at least:
- who the controller is and how to contact them,
- what data you process and for which purposes,
- the legal basis for each purpose (Art. 6 GDPR),
- who receives the data, such as hosting, email, payment or analytics providers,
- whether data leaves the EU and on what basis,
- how long you keep it,
- which rights visitors have, including the right to complain to a supervisory authority.
Check: open your website with the browser's developer tools, list every service that loads, and compare that list with your privacy policy.
2. Cookies: consent first, then tracking
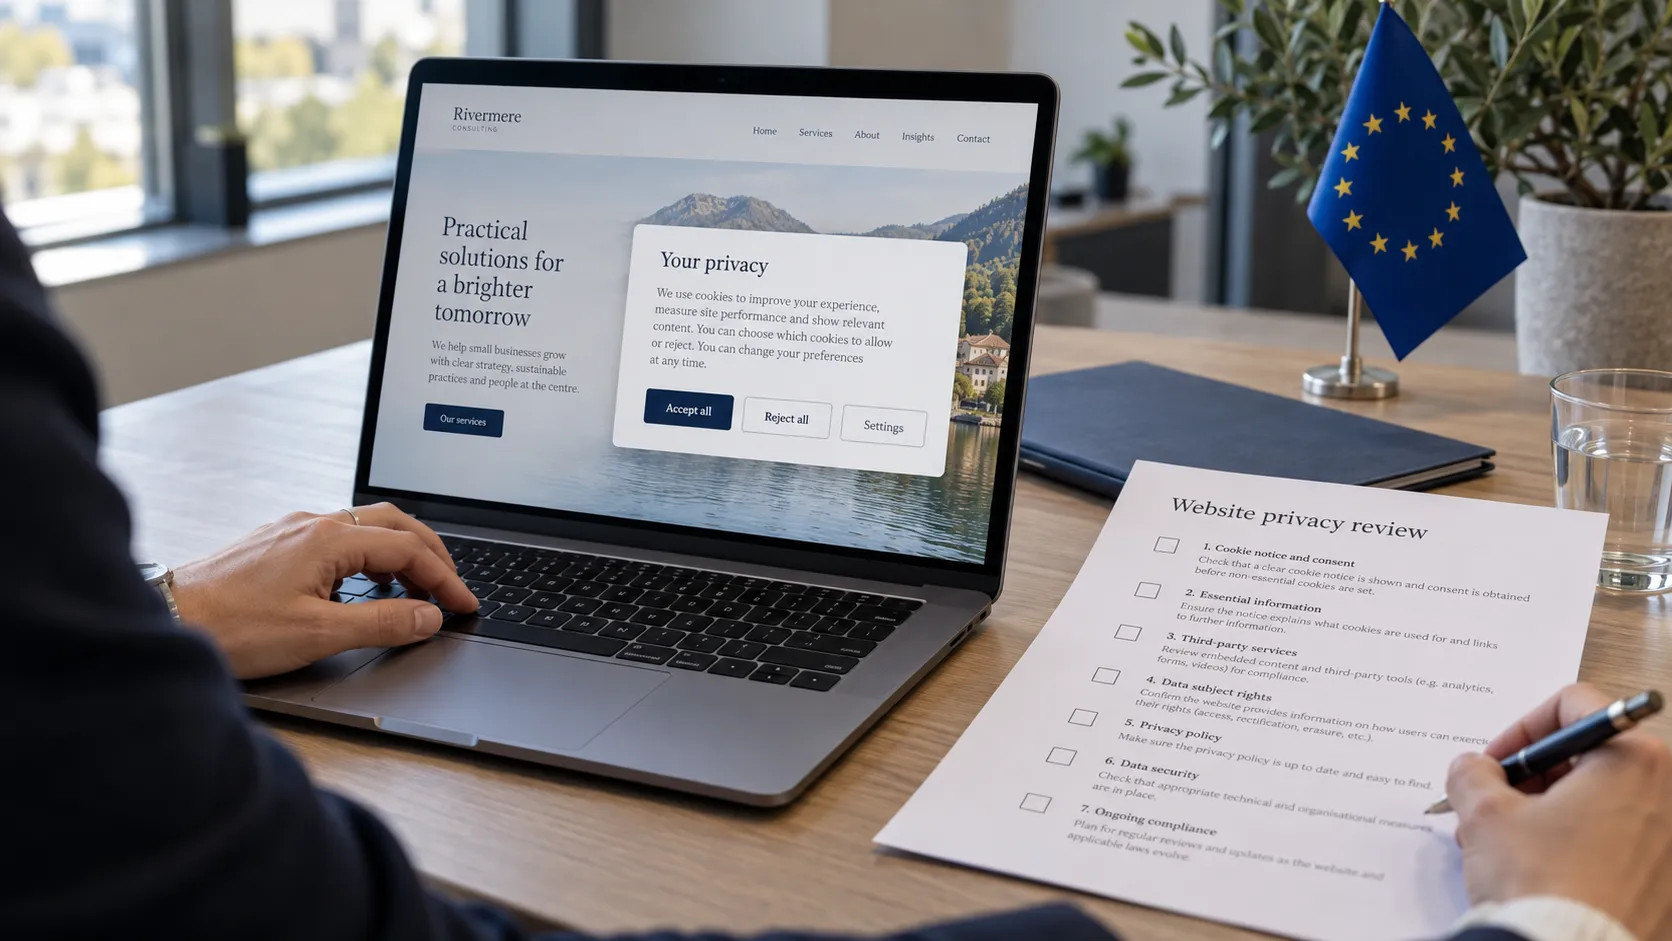
Strictly necessary cookies, for example a session cookie that keeps a contact form working, do not need consent. Analytics, advertising and most social media cookies do, and they must not be set before the visitor agrees. Since the Planet49 judgment of the Court of Justice of the EU (2019), pre-ticked boxes do not count as consent.
A compliant cookie banner:
- loads non-essential scripts only after consent,
- makes "Reject" as easy as "Accept",
- lets visitors change their decision later.
If your website uses no non-essential cookies at all, you do not need a consent banner. A short notice that explains this is enough.
3. Third-party content that loads in the background
This is the most common hidden problem. Google Fonts, embedded Google Maps, YouTube videos and social media widgets send the visitor's IP address to third parties as soon as the page loads. In 2022, the Regional Court of Munich awarded damages to a visitor because a website loaded Google Fonts from Google's servers without consent.
Fix: host fonts and icons on your own server, and load maps and videos only after a click, or replace them with a simple link.
Analytics tools work the same way: as long as no one has given consent, they should not load at all.
4. Contact forms: collect only what you need
Ask only for the data you need to answer: usually a name, an email address and a message. Mark optional fields clearly and link to your privacy policy next to the form. Send the form only over HTTPS, decide how long inquiries are kept, and then really delete old ones.
5. Hosting and service providers
Every provider that processes personal data for you, such as hosting, email, newsletter or CRM, needs a data processing agreement (Art. 28 GDPR). If the servers are outside the European Economic Area, the transfer also needs a legal basis, such as an adequacy decision or standard contractual clauses. The simplest solution is often a provider with servers in the EU.
6. Company details and legal pages
Visitors must be able to see who runs the website. The exact requirements depend on your country. In Germany, this is the Impressum. In Poland, a limited liability company (sp. z o.o.) must also show its registry court and share capital. Link the privacy policy, terms and company details from every page, usually in the footer.
7. Security is part of compliance
The GDPR also requires "appropriate technical and organisational measures" (Art. 32 GDPR). For a website, this means HTTPS everywhere, regular updates of the CMS, framework and plugins, secure admin access and tested backups. An outdated plugin is not only a security risk: a data breach caused by it may have to be reported to the supervisory authority within 72 hours.
Summary
A GDPR-compliant website is less about long legal texts and more about technical decisions: what loads, where data goes and how long it stays. Check these seven points once a year and every time you add a new tool, and you will avoid most problems.
At ModCodePlus, we build websites on these principles from the start: fonts hosted locally, no tracking without consent and legal pages that describe what the site really does. Contact us if you would like us to review your website.